Malware log shows it went after Codex auth files and saved browser passwords
A Japanese user traced what an infection read from their machine.

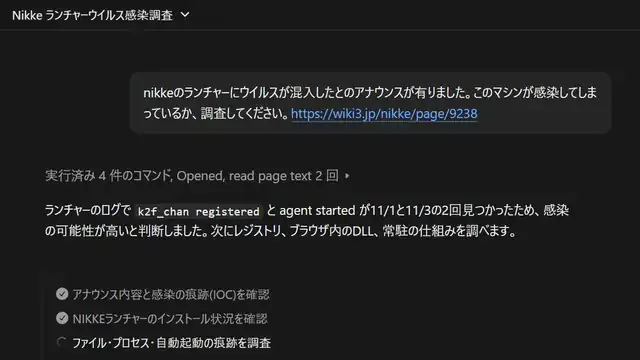
A user posting as @kokushing traced the logs of malware on their machine, posting in Japanese.
After a file called insight.bundle was downloaded, the malware read credentials and files including .codex/auth.json and config.toml, VS Code's settings.json, and saved Chrome and Edge passwords. They logged out of Codex and changed passwords right away.
The post drew about 570 likes.