Debian APT flaw let network attackers swap packages after verification and run code as root
The fix in apt 3.0.4 is four words long.

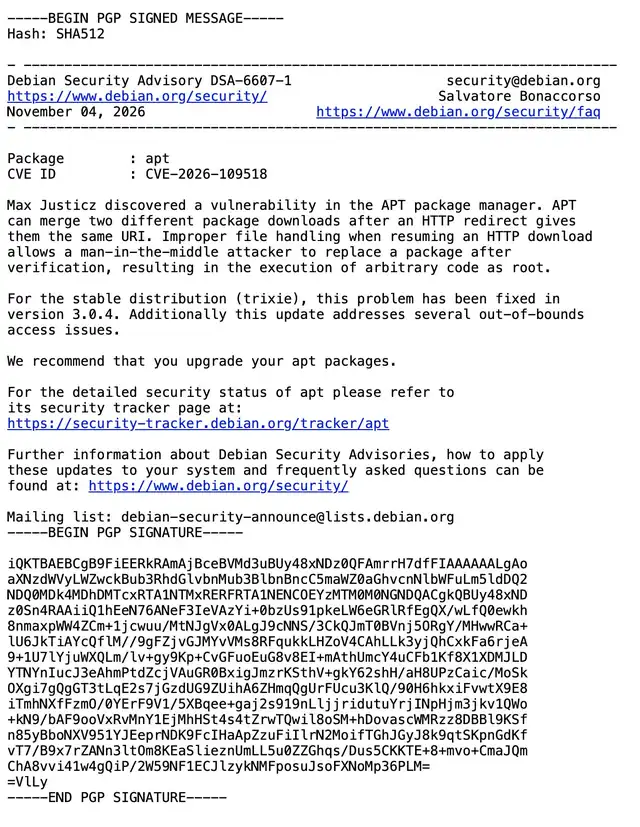
A flaw in APT, the tool that installs software on Debian Linux, let an attacker on the network tamper with a package after it passed verification and run code as root, according to International Cyber Digest (@IntCyberDigest).
The bug, CVE-2026-109518, sits in resumed HTTP downloads: APT could merge two different downloads when a redirect gave them the same address. Debian fixed it in apt 3.0.4, shipped to Debian 13 security updates on November 4.
Per Debian's changelog, the fix is four words: 'Open target files exclusively.' The post drew about 710 likes.