How eMudhra's 'most secure private key' broke
A post walks through the key export, a buggy script and a one-byte key.

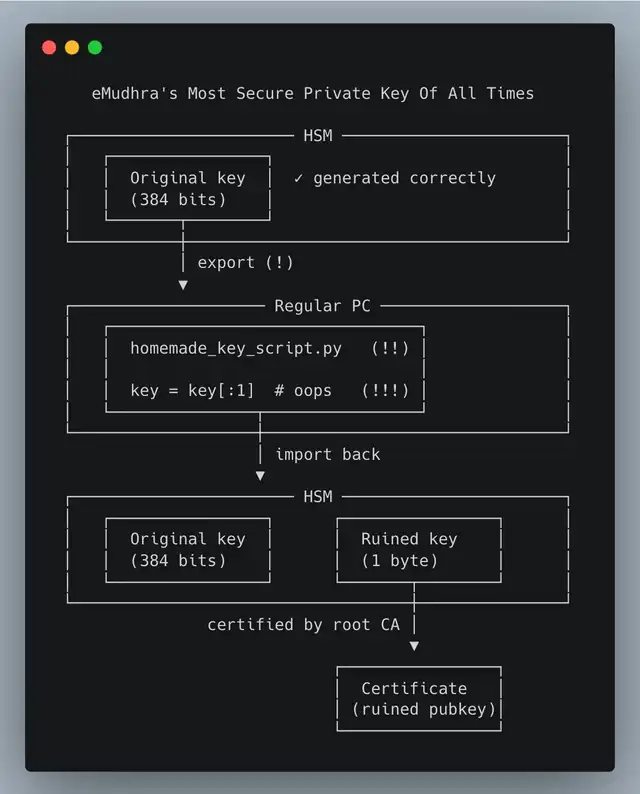
ohmypy (@ohmypy) described how certificate authority eMudhra handled its private key.
Per the post, they exported the private key from the hardware security module (HSM) to a regular PC, processed it with a Python script they wrote, and a bug truncated it to a single byte. They then imported the ruined key back into the HSM and certified it with the root CA.
Why it mattersThe whole point of an HSM is that the private key never leaves it.
The post drew about 708 likes by Wednesday afternoon.