Critical Synology NAS flaw let attackers read and write any file without logging in
A 9.8-rated SQL injection bug in the login system, plus an rsync flaw, are now patched.

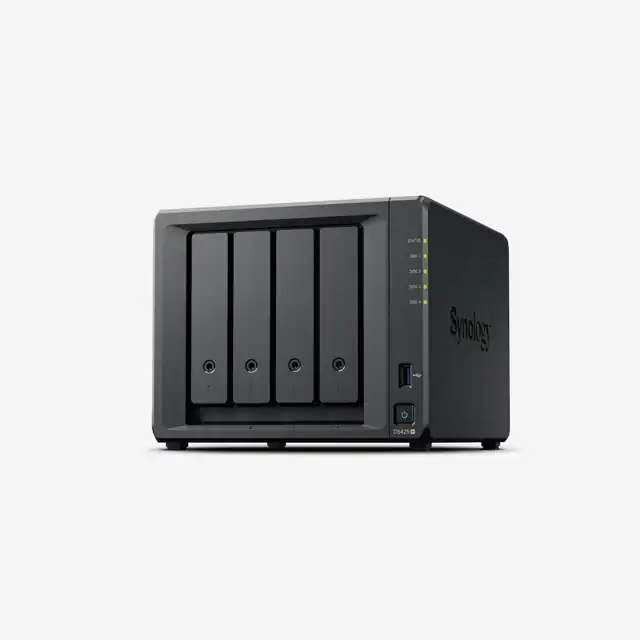
International Cyber Digest (@IntCyberDigest) reported on Wednesday a critical flaw in Synology NAS devices that lets attackers read and write any file on them without logging in. The bug is an SQL injection in the login system and scores 9.8 out of 10.
A second flaw, in rsync, also skips the login. According to the post, Synology patched both today and owners should update as soon as possible.
Why it mattersNAS boxes often hold a home's or small office's backups, so a no-login file read and write bug is about as bad as it gets.
The post drew about 1,770 likes by Wednesday morning.