Oracle rushes out emergency Java patch for a 9.1-severity trust flaw
CVE-2026-91403 breaks how Java apps decide which HTTPS certificates to trust.

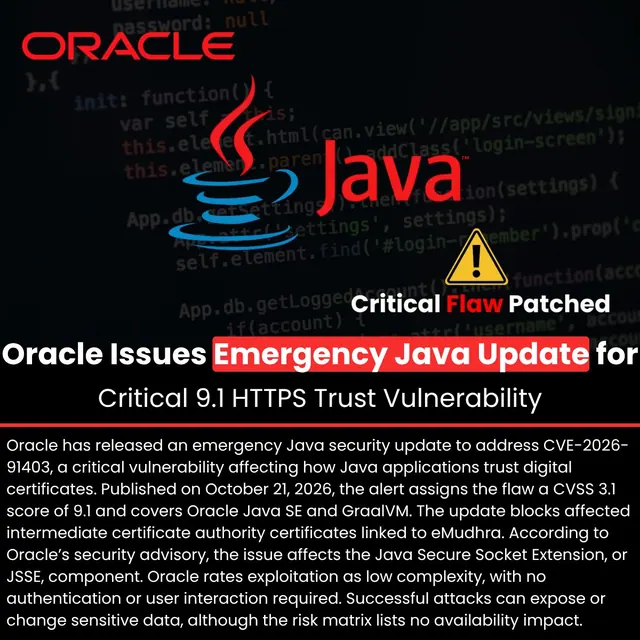
Oracle has released an emergency Java update for a critical HTTPS trust flaw, tracked as CVE-2026-91403 with a severity score of 9.1, according to Cyber Security News (@The_Cyber_News). The post says the bug lies in how Java applications decide which certificates to trust.
Certificates are what let an app confirm it is really talking to the server it expects. A flaw in that check could let an attacker pose as a trusted site and intercept or tamper with traffic.
Why it mattersJava runs inside a huge amount of enterprise software, and HTTPS trust is a foundation of secure connections. Teams running Java should look for Oracle's advisory and apply the update. With about 3,100 likes, it was one of the most-liked security items on today's board.