Google patches a Chrome zero-day already exploited in the wild
CVE-2026-125350 lets a remote attacker run code through Chrome's XML component.

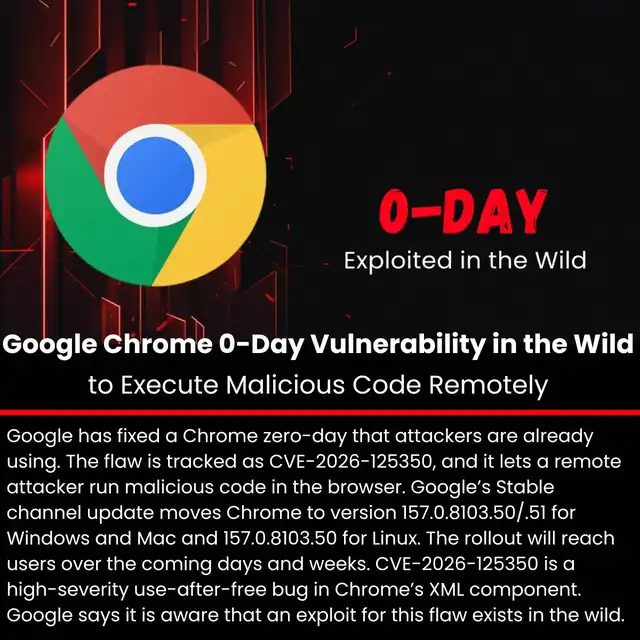
Cyber Security News (@The_Cyber_News) reported that Google fixed a Chrome zero-day that attackers are already using, tracked as CVE-2026-125350.
It is a high-severity use-after-free bug in Chrome's XML component that lets a remote attacker run malicious code in the browser. The Stable channel update moves Chrome to 157.0.8103.50/.51 on Windows and Mac and 157.0.8103.50 on Linux, rolling out over the coming days and weeks.
Why it mattersWith an exploit already in the wild, updating Chrome is the fix.
The post drew about 624 likes by Tuesday midday.